MCP Reference Servers v2.5.0 Fixes Eight Vulnerabilities — Six in mcp-server-git, Where an Untrusted Repo's Config Could Run Programs
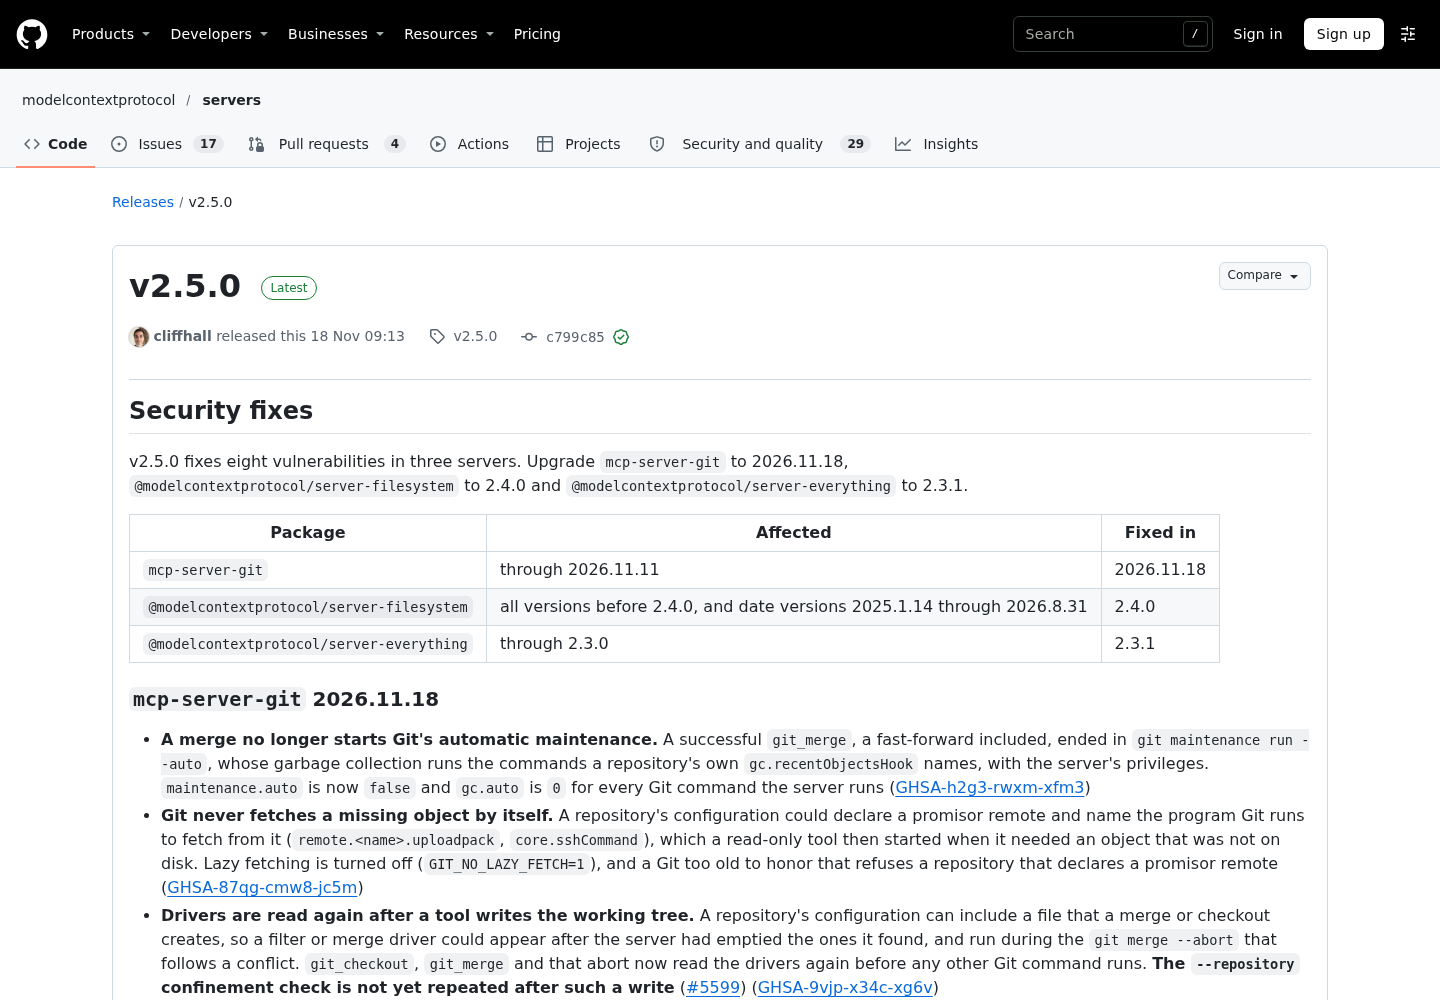
MCP reference servers v2.5.0 fixes eight vulnerabilities, six in mcp-server-git, where an untrusted repo's config or crafted index could run programs or leak files.
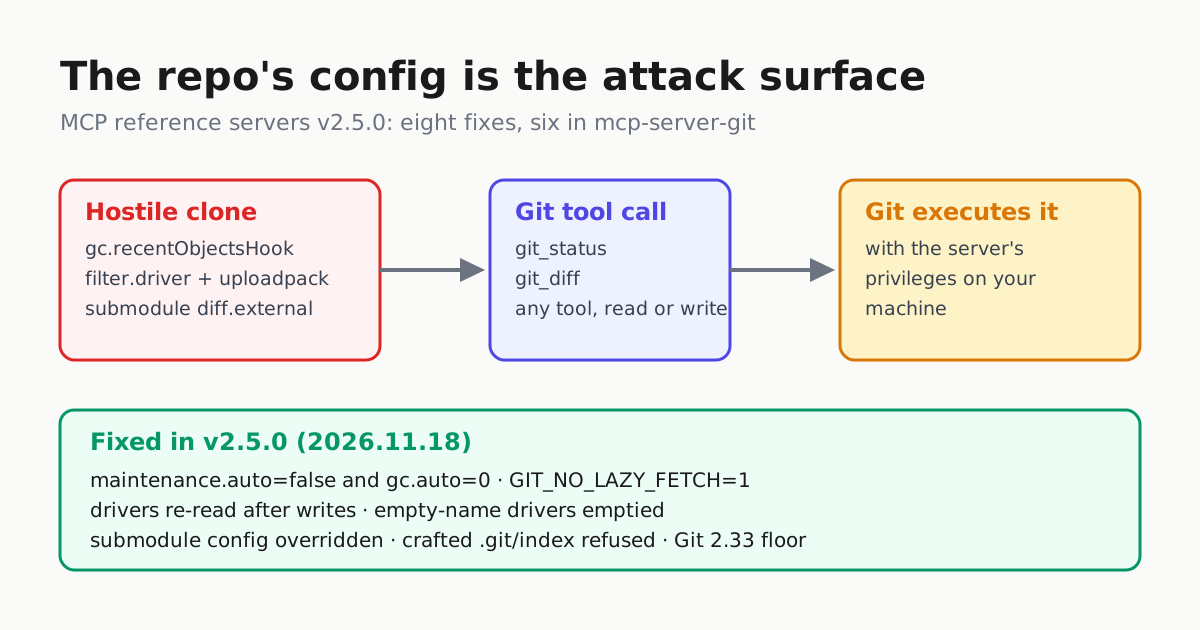
The official Model Context Protocol reference servers shipped v2.5.0 on Nov. 18 with eight security fixes across three servers. Six are in mcp-server-git — which the repository README describes as tools to read, search, and manipulate Git repositories, so it was never read-only — and in those six the trigger was the same: a repository’s own Git configuration or index deciding what a program on your machine runs or what a tool returns. Anyone who points Claude Code, Codex, Cursor or another MCP client at these servers to inspect an untrusted clone — a candidate dependency, a tutorial sample repo, a fork under review — is in the affected population.
A repo’s config decided what Git ran
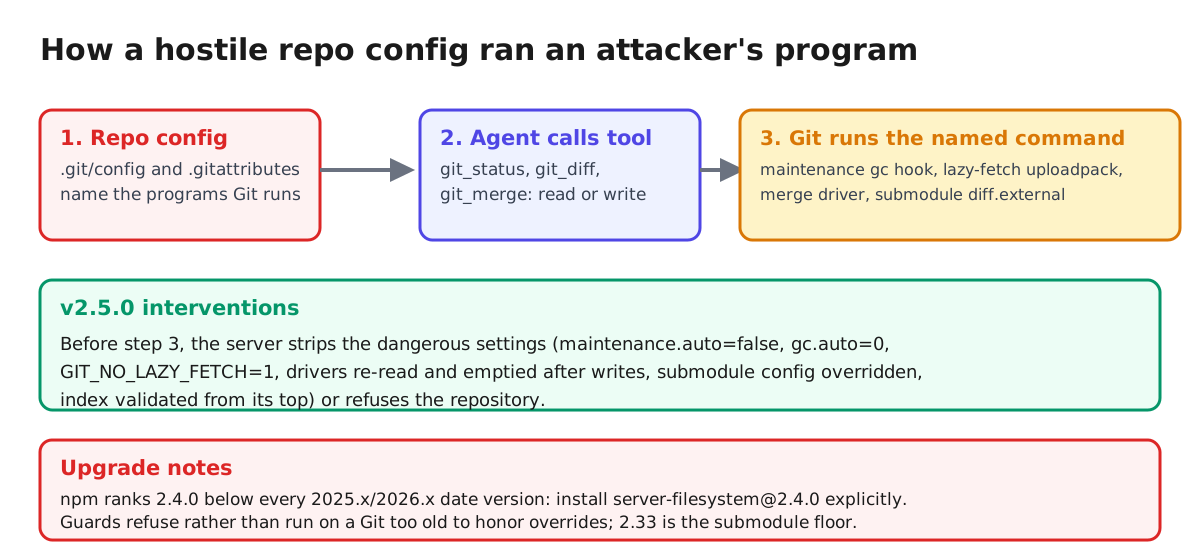
The pattern behind the six Git fixes is that a repository is a configuration surface: whatever tools an agent calls, Git itself may run the programs that repo’s config names. The release notes describe four execution paths a hostile clone could arm before or during a tool call:
- Merge triggers maintenance hooks. A successful
git_merge— a fast-forward included — ended ingit maintenance run --auto, whose garbage collection runs the commands a repository’s owngc.recentObjectsHooknames, with the server’s privileges. The server now forcesmaintenance.auto=falseandgc.auto=0on every Git command (GHSA-h2g3-rwxm-xfm3). - Lazy fetch runs a configured fetcher. Git never fetches a missing object by itself; a repo config could declare a promisor remote and name the program to fetch from it via
remote.<name>.uploadpackandcore.sshCommand. A read-only tool asking for an object not on disk would start it. Lazy fetching is now off (GIT_NO_LAZY_FETCH=1), and the notes say only that a Git too old to honor that refuses a repository declaring a promisor remote (GHSA-87qg-cmw8-jc5m). - Drivers appear mid-operation. A merge or checkout can create a file the repo config reads as a filter or merge driver, so a driver could appear after the server had emptied the ones it found, then run during the
git merge --abortafter a conflict.git_checkout,git_mergeand that abort now re-read the drivers first (GHSA-9vjp-x34c-xg6v) — though the release notes state that the--repositoryconfinement check is not yet repeated after such a write (issue #5599). An empty-name driver — Git accepts[filter ""], selected byfilter=in.gitattributes— was missed entirely and now is emptied too (GHSA-pm7p-vphh-2cg7). - Submodule config runs programs. With
diff.submodule=diff,git_diffran a nested diff inside each changed submodule under that submodule’s owndiff.externaland textconv drivers;git_checkoutandgit_addalso ran Git inside the submodule under its own config. The setting is nowshort, submodule-defined drivers are overridden, and Git older than 2.33 is refused where a submodule is checked out (GHSA-8wv7-r664-7594).
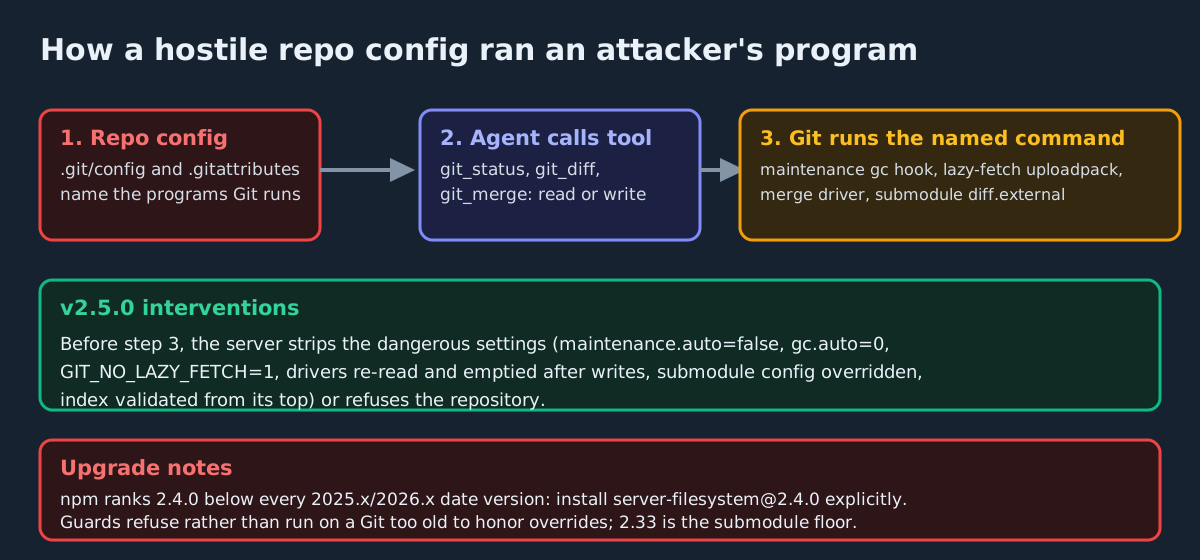
There is also a disclosure fix. A crafted .git/index naming a path like ../outside/secret made git_diff_unstaged and git_diff return that file’s content, and git_status report whether it exists — but only with --repository confinement. The index is now validated from its top before any tool reads it, and the untracked cache, which can name directories outside the working tree, is turned off (GHSA-r2q8-f657-4r56).
The other two fixes
server-filesystem 2.4.0 closes a symlink-swap race in listings on Linux and macOS: list_directory, list_directory_with_sizes, directory_tree and search_files checked a directory and then listed it through whatever it had become, so a swap could return the names of entries outside the allowed directories. Listings now happen in place against the checked directory. The release notes are explicit that a Windows listing is not yet anchored (issue #5600) (GHSA-rq2p-q7c4-6g27). For the confinement setup pattern — sharing one folder read-only and proving what a client can actually reach — see our MCP Filesystem Server read-only guide.
server-everything 2.3.1 fixes the gzip-file-as-resource private-address guard, which read NAT64 addresses in 64:ff9b::/96 as public, so on a network with a NAT64 gateway a URL could reach a private IPv4 address through one. The embedded IPv4 address is now checked (GHSA-38j4-j742-j7r3).
Upgrade notes that matter more than the version numbers
| Package | Affected | Fixed in |
|---|---|---|
| mcp-server-git (PyPI) | through 2026.11.11 | 2026.11.18 |
| @modelcontextprotocol/server-filesystem (npm) | all before 2.4.0, and 2025.1.14–2026.8.31 | 2.4.0 |
| @modelcontextprotocol/server-everything (npm) | through 2.3.0 | 2.3.1 |
Two things make this upgrade less routine than a version bump:
- npm will not offer the fix. The TypeScript servers moved from date versions (2025.x, 2026.x) to semantic versions at 1.0.0, and package managers rank 2.4.0 below every date version. If you installed a date version of server-filesystem,
npm install @modelcontextprotocol/server-filesystem@2.4.0explicitly — a routinenpm updatewill silently keep you vulnerable. - The Git guards now refuse instead of run. For the promisor-remote fix, v2.5.0 names no minimum Git version — a Git too old to honor
GIT_NO_LAZY_FETCHrefuses the repository. The one number in this release is Git 2.33, the floor below which submodule overrides are not passed and the repository is refused. On affected repos an older host Git now stops with a tool error where it previously ran the repo-named program — the right direction, but unattended lanes will see refusals. (The separate Git 2.31 floor for config overrides dates from v2.4.0 on Nov. 11, GHSA-6hqx-gqrx-c5r2.)
This is the second consecutive security release for these servers: v2.4.0 fixed six more, including a repo’s .git/config (fsmonitor, diff.external, hooks, filter and merge drivers) making the server run programs during read-only calls like git_status. v2.5.0 closes the gaps that survived that pass — drivers re-read after writes, empty-name drivers, submodule config, maintenance hooks and lazy fetch. The trajectory says these servers should be treated as under active adversarial review, not stable plumbing.
That matches how the maintainers describe the project: the repository README states the reference servers are educational examples “not as production-ready solutions,” and that developers should implement safeguards based on their own threat model. The practical takeaway for operators:
- Pin
mcp-server-gitat 2026.11.18, server-filesystem at 2.4.0 and server-everything at 2.3.1 in every MCP client config, and verify withuvx/pipandnpm lsrather than trusting the resolver. - Treat any clone of an untrusted repo that an agent can call Git tools against as hostile input until the pin lands — the pre-fix servers executed repo-named programs with your user’s privileges on what looked like a harmless diff or status call.
- Expect two documented gaps to remain: the
--repositoryconfinement check is not yet repeated after a write (#5599), and on Windows the filesystem listing race is still partly open (#5600).
For the broader hardening picture — least-privilege server config, read-only roles, and why a tool label is not a security boundary — see our guide on hardening MCP in production.
The fixes were credited to community reporters including zachariah-mithani, pterpen, YusefSyed, louislaurent1, ZackaryLoevseth and reservoir-cmyk, and the release tag commit is signed with GitHub’s verified signature.