Unofficial API or Official Connector: The Five-Rung Access Ladder for AI Agents After Reddit's API Shutdown
Reddit's API shutdown put dates on scraping lanes. Climb five rungs from official connector to wrapped session, and log every lane that risks an account.

Go deeper. Build your own.
Reddit has put dates on its open doors. New requests for public API access stop on Oct 31, RSS feeds end on Nov 13, and apps that never registered are cut off on Jan 12, 2027. Every AI agent that reads Reddit through one of those doors now has a deadline, and the quickest fix on offer, an unofficial API built by letting the agent drive somebody’s logged-in browser session, moves the risk from the platform’s servers onto that somebody’s account.
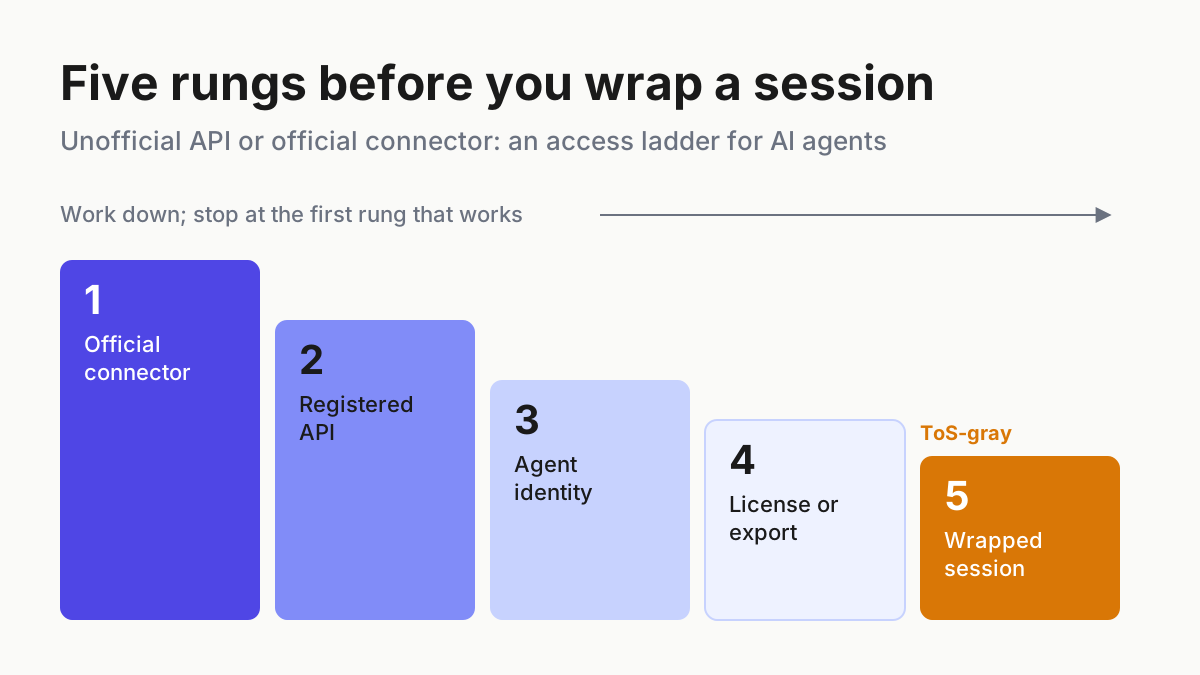
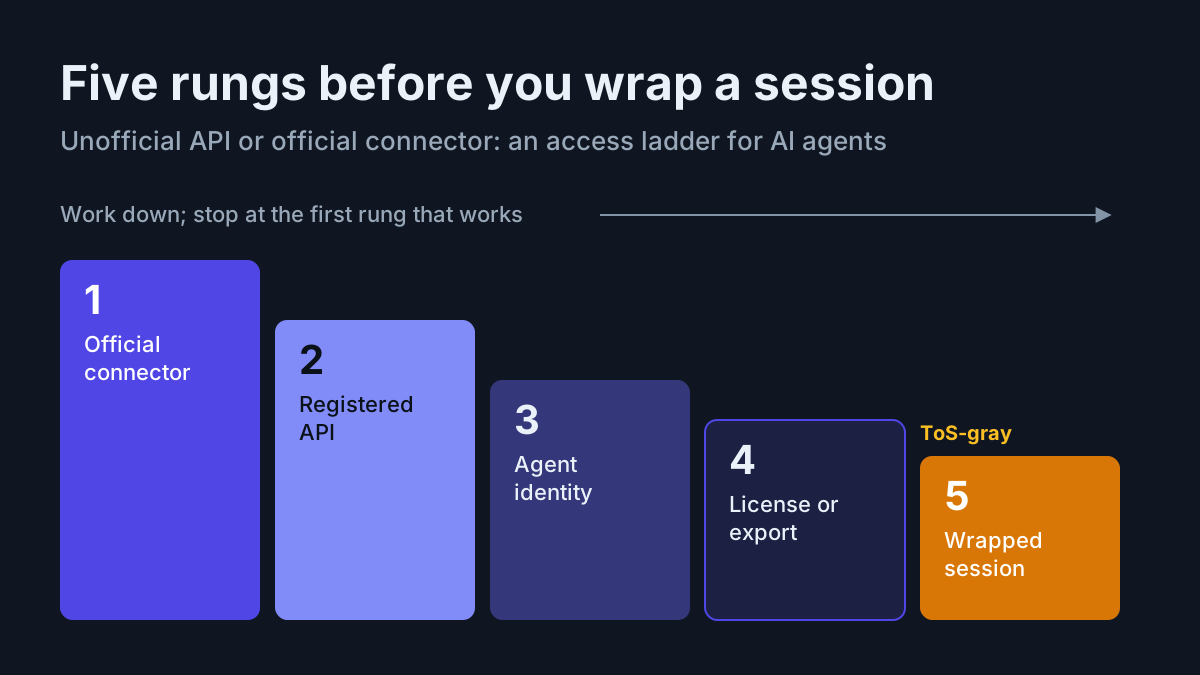
Don’t start there. For each data source an agent touches, work down a five-rung access ladder and stop at the first rung that works: an official connector or MCP server, an official API under a registered app, a sanctioned agent identity on the open web, a data license or export, and only then a wrapped session, labeled ToS-gray, on a secondary account, with a named owner and an expiry date. Every lane on the bottom rung gets a row in an account-risk ledger, and the platform’s own policy dates become your drill dates.
This is a decision method. It won’t tell you how to avoid detection, export a session or pick a wrapper, and it isn’t legal advice.
Reddit’s API shutdown and September’s other access changes
Reddit announced the wind-down on Sep 30 in r/modnews and r/redditdev. As reported by The Next Web and Decrypt, public Data API access stops taking new requests on Oct 31, 2026, RSS ends on Nov 13, unregistered apps lose access on Jan 12, 2027, and public API access ends in March 2027. Reddit’s stated reason was that “RSS is now widely used for large-scale scraping and automated abuse,” and its advice to most feed users was blunt: “If you use RSS for feeds outside of a community you moderate, there is no replacement” (TNW). The route Reddit points developers to is its Developer Platform, with a $1 million migration fund paying $1,000 per eligible app and applications due Nov 30 (Decrypt).
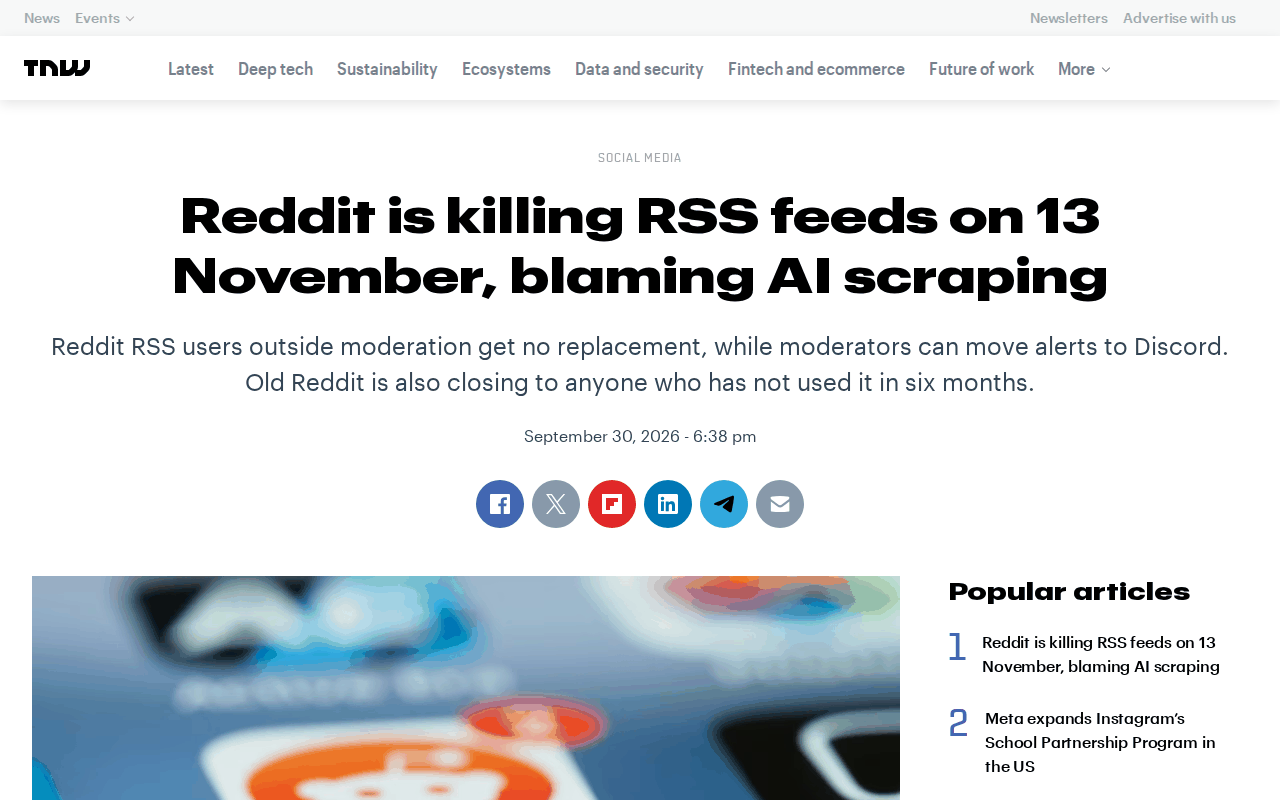 Screenshot: The Next Web, “Reddit is killing RSS feeds on 13 November, blaming AI scraping” (Sep 30, 2026), captured Oct 5, 2026.
The workaround was on sale within days. By Oct 5 at least one vendor was pitching a browser-extension MCP server that drives a user’s logged-in Reddit session as the practical answer, and describing the official route as expensive and slow. That pitch is the bottom rung of the ladder below, and it is usually the first option a team gets offered.
The open web is tightening in parallel. On Sep 15 Cloudflare changed its recommended defaults for newly onboarded ad-supported sites to “Disallow AI Training” for training crawlers and “Block on pages with ads” for agents, on the reasoning that “ad revenue depends on a human actually seeing the page.” Cloudflare also said it has no dedicated “Disallow” setting for agents yet, because the standards to support one are missing (Cloudflare).
 Screenshot: The Cloudflare Blog, “Have it both ways: stay discoverable in search while disallowing AI training” (Sep 15, 2026), captured Oct 5, 2026.
Two more facts set the stakes. On Aug 4 the Ninth Circuit, in Amazon v. Perplexity, vacated the injunction against Perplexity’s Comet browser and, as quoted in WSGR’s analysis of the opinion, wrote: “It is the user who ‘accesses’ Amazon’s computers, with the help of the Assistant.” The court left open the terms-of-service and contract claims, account termination, trespass and DMCA anti-circumvention (WSGR; Retail Insight Network). Read narrowly, the ruling placed the access with the user, so the remedies a platform keeps, ending the account and enforcing its terms, land on the user as well; it did not say that wrapping a session is permitted.
Meanwhile the top rung keeps widening: Anthropic’s Claude Marketplace opened on Sep 23 with “over 2,000 connectors and plugins” (Claude).
Why an agent on a wrapped session is not a person in a browser
A person reading a platform in a browser and an agent reading it through the same session send the same cookies, but they don’t behave the same. The agent runs at 3 a.m., opens a thousand threads, retries on every error and never gets bored, and platforms are built to notice exactly that. When they act, they act on the account. The unofficial AI wrappers piece states the rule for consumer AI logins: the account is the collateral. It holds the same way when an agent operates a third-party platform or SaaS tool on someone’s behalf.
So the access lane is a design decision, made once per data source by someone who can name whose account is at risk. The ladder is how you make it.
The five-rung agent access ladder, step by step
Step 1: List every data source and the lane each agent uses today
Start with what exists. For each agent, list the platforms and data sources it reads from or writes to, and how: connector, API key, feed, export file or a browser session. Then write down whose credential the lane runs on.
| Data source | Agent | Lane today | Whose credential | Rung or status |
|---|---|---|---|---|
| Reddit, public threads | Research digest | RSS feeds | None | Breaks Nov 13 |
| Reddit, one subreddit | Community monitor | Script on the public API, unregistered | A team member’s API key | Breaks Jan 12, 2027 |
| CRM | Sales assistant | Vendor MCP server over OAuth | Service account | 1 |
| Competitor pricing pages | Market scan | Headless browser, generic user agent | None | Unrated |
| Supplier portal | Ops agent | Wrapped session in a browser profile | An employee’s own login | 5 |
Rows are illustrative. The column that matters most is “whose credential”. Any row where the answer is a named person’s own login is a rung-5 lane, whatever the team calls it, and any row with “none” on the open web needs a rung-3 decision about how the agent identifies itself.
Don’t build the list from memory. Ask each agent’s owner three questions in writing: which sites and tools does it reach, does it ever sign in as anyone, and what happens to it if that platform changes its terms tomorrow. Then read the agent’s own configuration for connector entries, API keys and browser profiles. The lanes nobody mentions are almost always the rung-5 ones, because they started as a favor.
Step 2: Work down the ladder and stop at the first rung that works
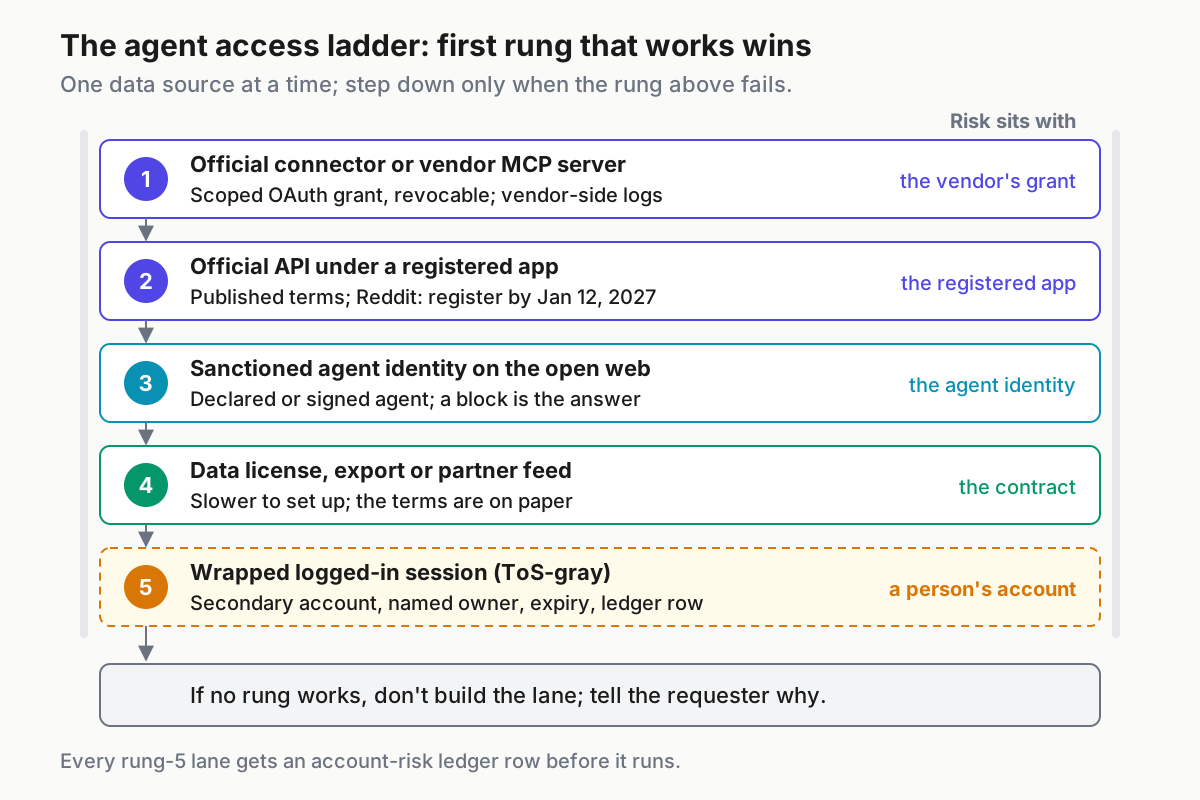
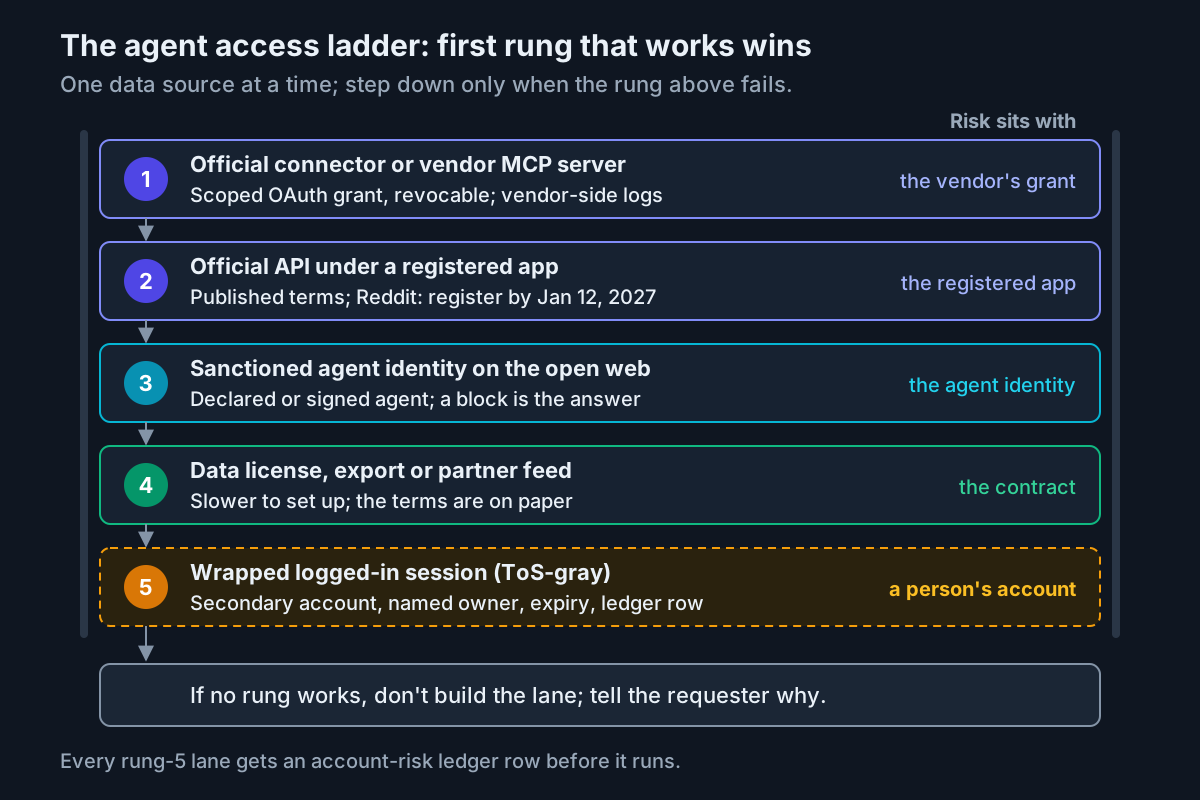 MCP connector vs browser automation, settled per data source: try each rung in order and record where the risk sits.
Define “works” before you start, because every team stretches it: a rung works when it returns the data the job needs, within the platform’s published terms, at a cost and lead time the job’s owner signs off. It doesn’t stop working because it costs money, needs an approval form or caps you at a rate lower than a scraper could manage. Those are prices, and the bottom rung has prices too; they are just charged to someone’s account later. Write the reason next to each rung you skip.
Rung 1: official connector or vendor MCP server
The vendor issued the credential, scoped it and logs the calls on its side, so revoking access is one action in an admin console and an incident leaves two audit trails instead of none. Check the vendor’s own connector list and the large marketplaces before anything else. A connector you adopt joins your MCP server inventory like any other server, with an owner and a review date.
Rung 2: official API under a registered app
You get published terms, rate limits you can plan around and a developer channel that announces changes before they land. It may cost money and approval time. For Reddit this is the lane to be on before Jan 12, 2027, and the Developer Platform migration fund is worth an application before Nov 30 if your app qualifies. Register the app to an organization identity, never to one person; service principals for agents covers why.
Rung 3: sanctioned agent identity on the open web
When there is no API, read public pages as a declared agent: a user agent that names your organization and a contact, and signed requests where the site supports them. Cloudflare’s signed-agents program uses Web Bot Auth, which signs HTTP requests so a site can verify who is calling, and the IETF webbotauth working group is turning that into a standard (Cloudflare; IETF). Expect to be classified, rate limited or blocked under defaults like Cloudflare’s Sep 15 change; on this rung a block is the site’s answer, so move to rung 4 or drop the source. If the agent only needs a page’s text, fetching to Markdown before driving a browser is usually enough.
Rung 4: data license, export or partner feed
This covers a user’s own data export, a licensed dataset or a partner feed under contract. It is slower to set up and rarely real-time, but the terms are on paper and nobody’s personal account is exposed. For historical research, a dated export beats a live scrape on both cost and reproducibility.
Rung 5: wrapping a logged-in session, last and labeled
An agent operating a real user session through a browser or extension is an unofficial API, whatever the vendor calls it. Sometimes nothing else exists, such as a supplier portal with no API and no export. It is allowed only with four conditions met: the lane is labeled ToS-gray in the inventory; it runs on a secondary account created for the purpose, never a person’s main account and never an admin; a named owner accepts the account risk in writing; and it has an expiry date by which it is replaced or killed. Who holds the cookies and where they live is covered in cookie custody; the ladder only decides whether the lane should exist.
Step 3: Match the job to a starting rung before anyone builds
Most bad lanes start as a quick script for one job. Settle the starting rung by job type before the script exists.
| Job | Start at | Lowest acceptable rung | Never |
|---|---|---|---|
| Act inside a SaaS tool you already pay for | 1 | 2 | 5 on an admin account |
| Read public posts for research | 2 | 4 | 5 |
| Watch public web pages for changes | 3 | 4 | Working around a block |
| Pull your own account’s data | 1 or 4 (export) | 4 | 5 on anyone else’s account |
| Operate a portal with no API or export | 1, if one appears | 5, with a ledger row | 5 without an owner and expiry |
| Post or write on a platform | 1 or 2 | 2 | 5 |
Writes deserve the hardest line. A wrapped session that reads is a terms-of-service problem; a wrapped session that posts, messages or buys speaks in a person’s name. Keep every rung-5 lane read-only, and send any job that writes through rungs 1 or 2, the same rule that applies when a merchant refuses a checkout agent.
Step 4: Open an account-risk ledger row for every rung-5 lane
Each lane on the bottom rung gets one row before it runs, and the row is what you review, not the code. The example below is illustrative and shows the fields filled for a Reddit lane, the kind of row that should not survive the next six months.
| Field | What to write | Illustrative example |
|---|---|---|
| Platform | Service and surface | Reddit, logged-in web |
| Whose account | A secondary account, never a person’s main | research-agent-02 |
| Lane | How the agent reaches it, and read or write | Wrapped browser session, read-only |
| ToS clause | The clause covering automated access, quoted with the date you read it | Quoted and dated in the row |
| Policy dates that break it | Every announced date for the platform | Oct 31, Nov 13, Jan 12, 2027, March 2027 |
| Replacement rung | The rung you are moving to, and when | Rung 2, registered app, before Jan 12 |
| Kill switch | Revoke the session, delete stored cookies, disable the job | Owner can do all three in five minutes |
| Owner | A person who accepts the account risk | Named in the row |
| Expiry | The date the lane dies if not replaced | 90 days from opening |
A row with an empty owner, replacement rung or expiry doesn’t get approved. A row past its expiry gets killed on that date, not discussed.
Whoever approves the row asks five questions, and every answer has to be yes:
- Did someone check rungs 1 to 4 and write down why each one fails for this job?
- Is the account a secondary one, created for this lane, with no admin rights and no payment method attached?
- Is the lane read-only, with no path to post, message or buy?
- Can the owner run the kill switch alone, without the person who wrote the agent?
- Is the expiry within the next platform policy date, or ninety days, whichever comes first?
Step 5: Turn the platform’s policy dates into drill dates
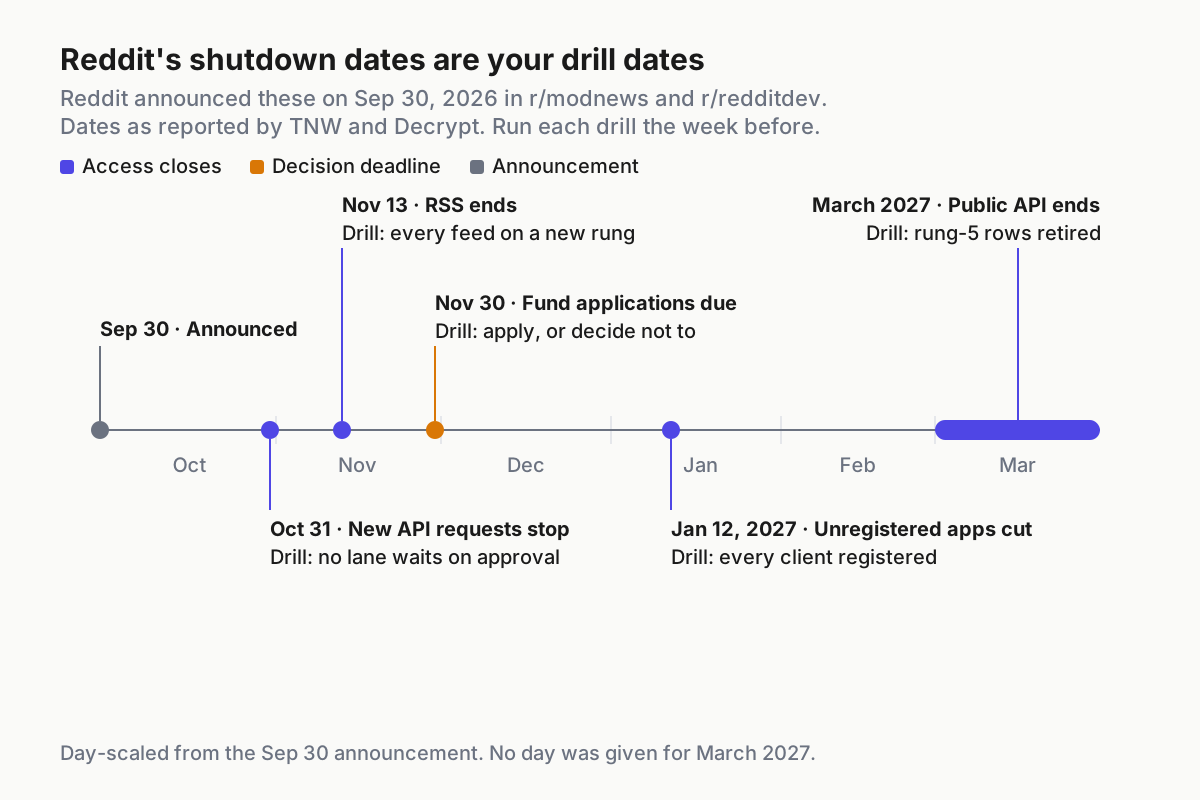
 Reddit API shutdown dates for AI agents, as reported by TNW and Decrypt; each one is a drill the week before.
A platform that publishes dates has written your schedule. Put each one on the calendar as a drill the week before, and run the same three moves every time: list the lanes that depend on what is ending, confirm the replacement rung is live and returning the same data, then switch and kill the old lane on the date.
| Date | What ends | Drill the week before |
|---|---|---|
| Oct 31, 2026 | New public API access requests | Any lane still waiting on an approval gets a fallback rung |
| Nov 13, 2026 | RSS feeds | Every feed reader moved to rung 2 or rung 4 |
| Nov 30, 2026 | Migration fund applications (per Decrypt) | Apply, or record the decision not to |
| Jan 12, 2027 | Access for unregistered apps | Every client registered to an organization identity |
| March 2027 | Public API access | Every Reddit rung-5 row retired or replaced |
The same drill works for any platform. When a vendor announces a deprecation, the dates go into the ledger’s “policy dates” column the day they’re published, and the drills go on the calendar that afternoon.
Step 6: Re-check rung-5 rows weekly and kill the expired ones
Give the ledger fifteen minutes a week. For each rung-5 row, re-read the platform’s developer announcements and terms page, update the policy dates, and check whether the replacement rung has opened. Kill any row past its expiry: revoke the session, delete the stored cookies, disable the job and note the date. Report one number upward, the count of open rung-5 rows, and expect it to fall.
The ladder moves in both directions, so re-rank when a platform opens a door as well as when it shuts one. If a vendor ships a connector or an MCP server for a source you reach on rung 3, 4 or 5, every lane for that source gets a migration date the same week. The coverage of Reddit’s Sep 30 announcement mentions no agent connector, and as of Oct 5 the Reddit MCP servers in circulation are community-built; if an official one ships, every Reddit row in your ledger moves up.
Failure modes on unofficial lanes, and the signal for each
Rung-5 lanes fail loudly for the platform and quietly for you. Put each signal where someone will see it before the account owner does.
| Failure | Signal | First move |
|---|---|---|
| Account restricted or banned | Login challenge, suspension notice, sudden 401s | Stop the job; the owner contacts the platform as themselves |
| Silent data drift after a site change | Empty fields, parse errors, record counts falling | Pause, compare against a manual read, check for an official rung |
| Policy date passes | 403s or empty responses on the date | Switch to the replacement rung; if none is live, the lane is dead |
| Edge block on the open web | Challenge pages or block responses at a site | Treat it as a “no”; move down the ladder or drop the source |
| Session used somewhere unexpected | Platform security alert, a login from an unknown location | Revoke the session and rotate the account password |
| Read lane starts writing | Posts or messages from the account nobody sent | Kill the lane; review who changed its scope |
The drift row is the expensive one. A wrapped session rarely errors when a page changes; it returns less, and an agent summarizing “less” writes a confident digest of half the data. Track the record count per run and alert on a drop, not just on failures.
Access lanes belong in the fleet inventory
The rung an agent stands on is as much a property of that agent as its model, its permission mode or its owner, and it belongs in the same place you keep those. If your fleet view can show which agents are waiting on you but not which ones run on a person’s login, it is missing the row most likely to cause a bad week. Put the rung and the ledger link next to each agent in your command center for running many agents, so stopping an agent and killing its lane are the same motion.
Reddit’s dates make this concrete for one platform this quarter. The next platform won’t announce as clearly, which is why the ladder and the ledger should already exist when it changes the rules.
FAQ
Is it legal for an AI agent to use my logged-in session on a website?
This isn’t legal advice. In Amazon v. Perplexity the Ninth Circuit said it is the user who accesses the site with the agent’s help, and it left terms-of-service claims and account termination open. A platform can still act against the account under its terms, so the account holder carries that risk.
What happens to AI agents when Reddit’s public API shuts down?
Agents reading Reddit RSS lose it on Nov 13, 2026. Apps that never registered are cut off on Jan 12, 2027, and public API access ends in March 2027. Move each lane to a registered app, Reddit’s Developer Platform, or a license or export before those dates, and kill the rest.
MCP connector vs browser automation: which should an agent use?
Use the official connector or MCP server whenever one exists, because the vendor scopes the grant, logs the calls and lets you revoke access in one place. Browser automation of a logged-in session is the last rung, for sources with no official route, on a secondary account with an owner and expiry.
Sources
- The Next Web: Reddit is killing RSS feeds on 13 November, blaming AI scraping (Sep 30, 2026)
- Decrypt: Reddit killing RSS feeds and public API access (Oct 1, 2026)
- Cloudflare: Have it both ways, accountable mixed-use AI crawlers (Sep 15, 2026)
- WSGR Data Advisor: Ninth Circuit addresses CFAA and agentic AI tools (Aug 2026)
- Retail Insight Network: US court overturns Amazon injunction against Perplexity (Aug 5, 2026)
- Claude: Claude Marketplace (Sep 23, 2026)
- Cloudflare: The age of agents, cryptographically recognizing agent traffic (Aug 28, 2025)
- IETF: Web Bot Auth (webbotauth) working group (charter page, read Oct 5, 2026)